Oct
28
2020
--

Enso Security raises $6M for its application security posture management platform

Enso Security, a Tel Aviv-based startup that is building a new application security posture management platform, today announced that it has raised a $6 million seed funding round led by YL Ventures, with participation from Jump Capital. Angel investors in this round include HackerOne co-founder and CTO Alex Rice; Sounil Yu, the former chief security scientist at Bank of America; Omkhar Arasaratnam, the former head of Data Protection Technology at JPMorgan Chase and toDay Ventures.

The company was founded by Roy Erlich (CEO), Chen Gour Arie (CPO) and Barak Tawily (CTO). As is so often the case with Israeli security startups, the founding team includes former members of the Israeli Intelligence Corps, but also a lot of hands-on commercial experience. Erlich, for example, was previously the head of application security at Wix, while Gour Arie worked as an application security consultant for numerous companies across Europe and Tawily has a background in pentesting and led a security team at Wix, too.
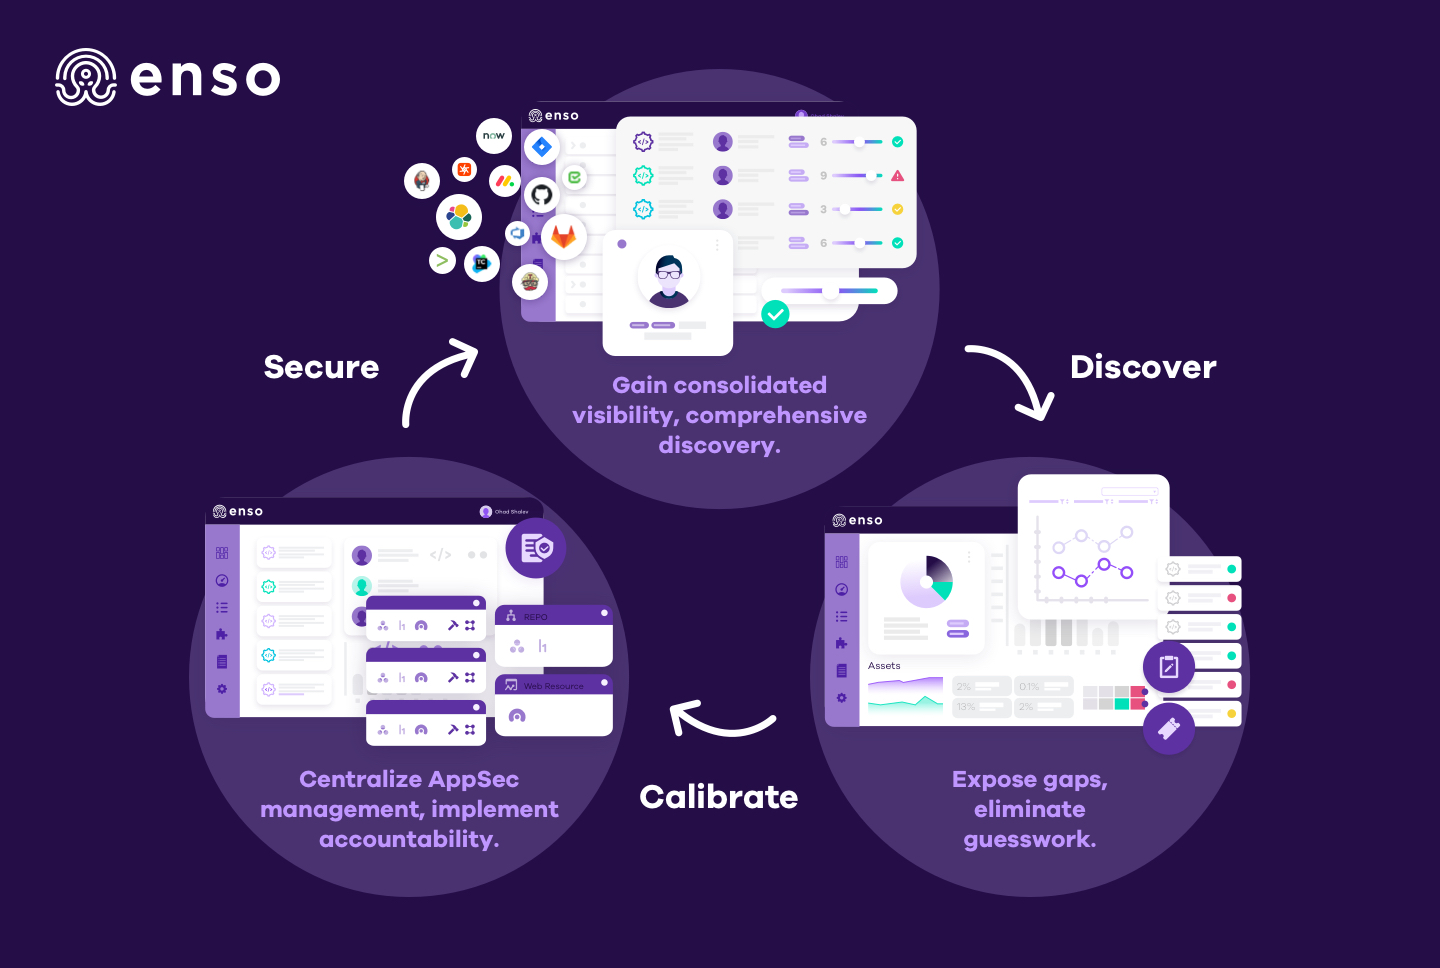
Image Credits: Enso Security / Getty Images

“It’s no secret that, today, the diversity of R&D allows [companies] to rapidly introduce new applications and push changes to existing ones,” Erlich explained. “But this great complexity for application security teams results in significant AppSec management challenges. These challenges include the difficulty of tracking applications across environments, measuring risks, prioritizing tasks and enforcing uniform Application Security strategies across all applications.”

But as companies push out code faster than ever, the application security teams aren’t able to keep up — and may not even know about every application being developed internally. The team argues that application security today is often a manual effort to identify owners and measure risk, for example — and the resources for application security teams are often limited, especially when compared the size of the overall development team in most companies. Indeed, the Enso team argues that most AppSec teams today spend most of their time creating relationships with developers and performing operational and product-related tasks — and not on application security.
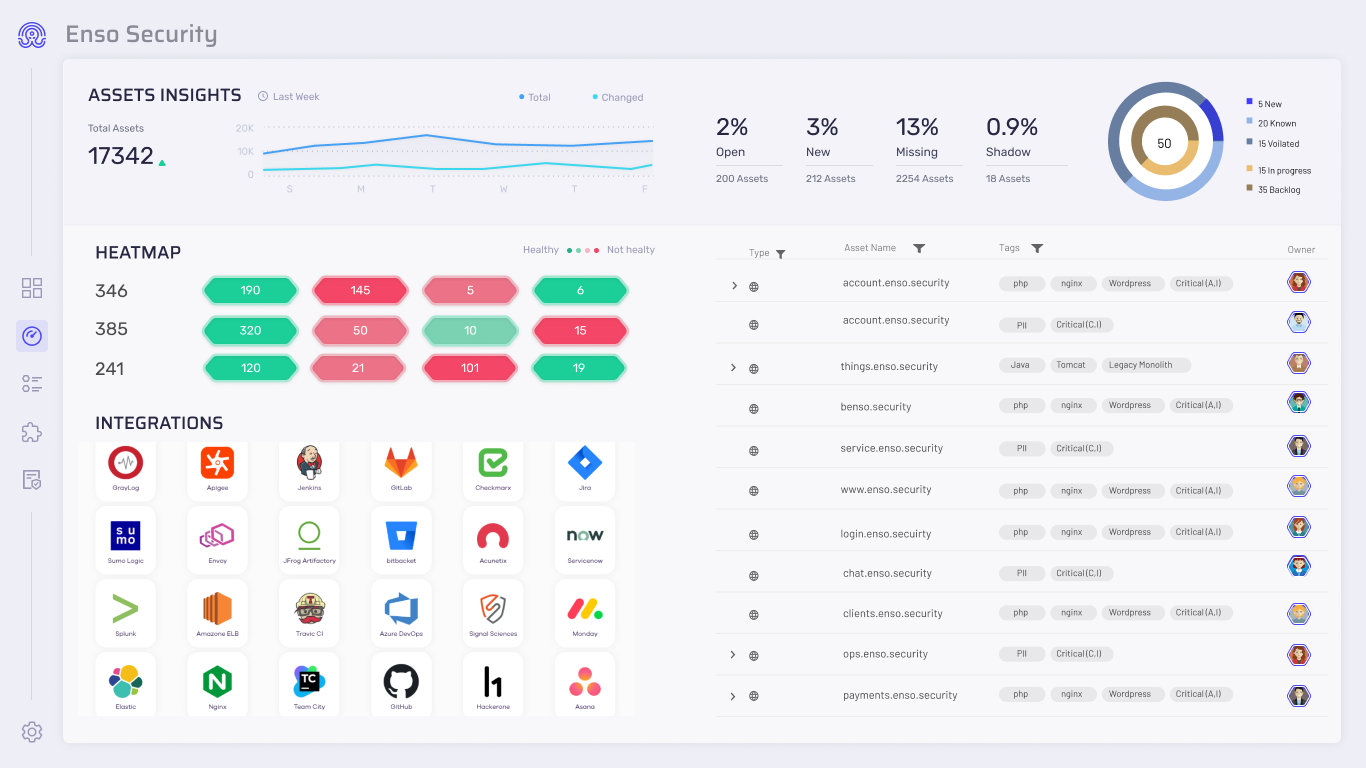
Image Credits: Enso Security / Getty Images

“It’s a losing fight from the application security side because you have no chance to cover everything,” Erlich noted. “Having said that, […] it’s all about managing the risk. You need to make sure that you take data-driven decisions and that you have all the data that you need in one place.”

Enso Security then wants to give these teams a platform that gives them a single pane of glass to discover applications, identify owners, detect changes and capture their security posture. From there, teams can then prioritize and track their tasks and get real-time feedback on what is happening across their tools. The company’s tools currently pull in data from a wide variety of tools, including the likes of JIRA, Jenkins, GitLab, GitHub, Splunk, ServiceNow and the Envoy edge and service proxy. But as the team argues, even getting data from just a few sources already provides benefits for Enso’s users.

Looking ahead, the team plans to continue improving its product and staff up from its small group of seven employees to about 20 in the next year.

“Roy, Chen and Barak have come up with a very elegant solution to a notoriously complex problem space,” said Ofer Schreiber, partner at YL Ventures . “Because they cut straight to visibility — the true heart of this issue — cybersecurity professionals can finally see and manage all of the applications in their environments. This will have an extraordinary impact on the rate of application rollout and enterprise productivity.”
Sep
08
2020
--

Google Cloud launches its Business Application Platform based on Apigee and AppSheet

Unlike some of its competitors, Google Cloud has recently started emphasizing how its large lineup of different services can be combined to solve common business problems. Instead of trying to sell individual services, Google is focusing on solutions and the latest effort here is what it calls its Business Application Platform, which combines the API management capabilities of Apigee with the no-code application development platform of AppSheet, which Google acquired earlier this year.

As part of this process, Google is also launching a number of new features for both services today. The company is launching the beta of a new API Gateway, built on top of the open-source Envoy project, for example. This is a fully managed service that is meant to make it easier for developers to secure and manage their API across Google’s cloud computing services and serverless offerings like Cloud Functions and Cloud Run. The new gateway, which has been in alpha for a while now, offers all the standard features you’d expect, including authentication, key validation and rate limiting.

As for its low-code service AppSheet, the Google Cloud team is now making it easier to bring in data from third-party applications thanks to the general availability to Apigee as a data source for the service. AppSheet already supported standard sources like MySQL, Salesforce and G Suite, but this new feature adds a lot of flexibility to the service.

With more data comes more complexity, so AppSheet is also launching new tools for automating processes inside the service today, thanks to the early access launch of AppSheet Automation. Like the rest of AppSheet, the promise here is that developers won’t have to write any code. Instead, AppSheet Automation provides a visual interface, that, according to Google, “provides contextual suggestions based on natural language inputs.” 

“We are confident the new category of business application platforms will help empower both technical and line of business developers with the core ability to create and extend applications, build and automate workflows, and connect and modernize applications,” Google notes in today’s announcement. And indeed, this looks like a smart way to combine the no-code environment of AppSheet with the power of Apigee .

Jun
30
2020
--

Kong donates its Kuma control plane to the Cloud Native Computing Foundation

API management platform Kong today announced that it is donating its open-source Kuma control plane technology to the Cloud Native Computing Foundation (CNCF). Since Kong built Kuma on top of the Envoy service mesh — and Envoy is part of the CNCF’s stable of open-source projects — donating it to this specific foundation was likely an obvious move.

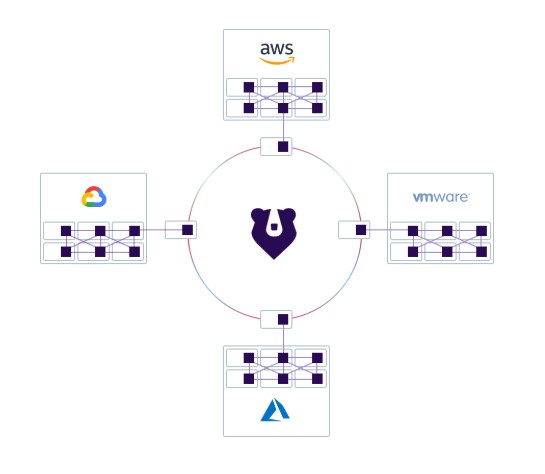
The company first open-sourced Kuma in September 2019. In addition to donating it to the CNCF, the company also today launched version 0.6 of the codebase, which introduces a new hybrid mode that enables Kuma-based service meshes to support applications that run on complex heterogeneous environments, including VMs, Kubernetes clusters and multiple data centers.

Image Credits: Kong

Kong co-founder and CTO Marco Palladino says that the goal was always to donate Kuma to the CNCF.

“The industry needs and deserves to have a cloud native, Envoy-based control plane that is open and not governed by a single commercial entity,” he writes in today’s announcement. “From a technology standpoint, it makes no sense for individual companies to create their own control plane but rather build their own unique applications on proven technologies like Envoy and Kuma. We welcome the broader community to join Kuma on Slack and on our bi-weekly community calls to contribute to the project and continue the incredible momentum we have achieved so far.”

Kuma will become a CNCF Sandbox project. The sandbox is the first stage that projects go through to become full graduated CNCF projects. Currently, the foundation is home to 31 sandbox projects, and Kong argues that Kuma is now production-ready and at the right stage where it can profit from the overall CNCF ecosystem.

“It’s truly remarkable to see the ecosystem around Envoy continue to develop, and as a vendor-neutral organization, CNCF is the ideal home for Kuma,” said Matt Klein, the creator of the Envoy proxy. “Now developers have access to the service mesh data plane they love with Envoy as well as a CNCF-hosted Envoy-based control plane with Kuma, offering a powerful combination to make it easier to create and manage cloud native applications.”

Dec
17
2019
--

Google details its approach to cloud-native security

Over the years, Google’s various whitepapers, detailing how the company solves specific problems at scale, have regularly spawned new startup ecosystems and changed how other enterprises think about scaling their own tools. Today, the company is publishing a new security whitepaper that details how it keeps its cloud-native architecture safe.

The name, BeyondProd, already indicates that this is an extension of the BeyondCorp zero trust system the company first introduced a few years ago. While BeyondCorp is about shifting security away from VPNs and firewalls on the perimeter to the individual users and devices, BeyondProd focuses on Google’s zero trust approach to how it connects machines, workloads and services.

Unsurprisingly, BeyondProd is based on pretty much the same principles as BeyondCorp, including network protection at the end, no mutual trust between services, trusted machines running known code, automated and standardized change rollout and isolated workloads. All of this, of course, focuses on securing cloud-native applications that generally communicate over APIs and run on modern infrastructure.

“Altogether, these controls mean that containers and the microservices running inside can be deployed, communicate with each other, and run next to each other, securely; without burdening individual microservice developers with the security and implementation details of the underlying infrastructure,” Google explains.

Google, of course, notes that it is making all of these features available to developers through its own services like GKE and Anthos, its hybrid cloud platform. In addition, though, the company also stresses that a lot of its open-source tools also allow enterprises to build systems that adhere to the same platforms, including the likes of Envoy, Istio, gVisor and others.

“In the same way that BeyondCorp helped us to evolve beyond a perimeter-based security model, BeyondProd represents a similar leap forward in our approach to production security,” Google says. “By applying the security principles in the BeyondProd model to your own cloud-native infrastructure, you can benefit from our experience, to strengthen the deployment of your workloads, how your their communications are secured, and how they affect other workloads.”

You can read the full whitepaper here.

Dec
11
2018
--

The Cloud Native Computing Foundation adds etcd to its open-source stable

The Cloud Native Computing Foundation (CNCF), the open-source home of projects like Kubernetes and Vitess, today announced that its technical committee has voted to bring a new project on board. That project is etcd, the distributed key-value store that was first developed by CoreOS (now owned by Red Hat, which in turn will soon be owned by IBM). Red Hat has now contributed this project to the CNCF.

Etcd, which is written in Go, is already a major component of many Kubernetes deployments, where it functions as a source of truth for coordinating clusters and managing the state of the system. Other open-source projects that use etcd include Cloud Foundry, and companies that use it in production include Alibaba, ING, Pinterest, Uber, The New York Times and Nordstrom.

“Kubernetes and many other projects like Cloud Foundry depend on etcd for reliable data storage. We’re excited to have etcd join CNCF as an incubation project and look forward to cultivating its community by improving its technical documentation, governance and more,” said Chris Aniszczyk, COO of CNCF, in today’s announcement. “Etcd is a fantastic addition to our community of projects.”

Today, etcd has well over 450 contributors and nine maintainers from eight different companies. The fact that it ended up at the CNCF is only logical, given that the foundation is also the host of Kubernetes. With this, the CNCF now plays host to 17 projects that fall under its “incubated technologies” umbrella. In addition to etcd, these include OpenTracing, Fluentd, Linkerd, gRPC, CoreDNS, containerd, rkt, CNI, Jaeger, Notary, TUF, Vitess, NATS Helm, Rook and Harbor. Kubernetes, Prometheus and Envoy have already graduated from this incubation stage.

That’s a lot of projects for one foundation to manage, but the CNCF community is also extraordinarily large. This week alone about 8,000 developers are converging on Seattle for KubeCon/CloudNativeCon, the organization’s biggest event yet, to talk all things containers. It surely helps that the CNCF has managed to bring competitors like AWS, Microsoft, Google, IBM and Oracle under a single roof to collaboratively work on building these new technologies. There is a risk of losing focus here, though, something that happened to the OpenStack project when it went through a similar growth and hype phase. It’ll be interesting to see how the CNCF will manage this as it brings on more projects (with Istio, the increasingly popular service mesh, being a likely candidate for coming over to the CNCF as well).

Powered by WordPress | Theme: Aeros 2.0 by TheBuckmaker.com